In general, collecting and analysing information that is genuinely public is not unlawful in India, and no Indian law bans OSINT as such. Whether a particular OSINT activity is lawful depends on four things: how the information is collected (public access or access-controlled), what it contains (especially personal data), who is doing it (a State agency or a private entity), and how it is stored, used and produced as evidence. The line is usually crossed not by looking at public material, but by bypassing access controls, intercepting communications, misusing personal data or ignoring the rules that govern evidence.
Key takeaways
- OSINT from truly public sources is generally lawful in India
- No single Indian law regulates OSINT by name, so several laws apply together
- Accessing systems or accounts without permission can breach the IT Act, even if the goal is investigation
- Interception and monitoring of communications need formal legal authority and are not OSINT
- “Publicly visible” is not the same as “free to use for any purpose” under data protection law
- The DPDP Act’s substantive obligations begin in May 2027, so preparation matters now
- State agencies work within investigation powers and the constitutional privacy test, and the DPDP Act has specific exemptions for them
- Documentation decides whether OSINT findings can be relied on later
What counts as OSINT, and what does not
OSINT means collecting and analysing information from sources that anyone can lawfully access. That includes news, public websites, public social media posts, public records, company filings, public forums and open-access databases.
It does not include:
- logging into someone else’s account
- breaking passwords or bypassing paywalls and other access controls
- hacking, or using stolen credentials
- intercepting calls, messages or network traffic
- reading private messages or closed spaces without lawful authority
Those activities belong to other legal categories, each with its own rules.
The laws that matter
No statute is called “the OSINT law”. These are the provisions that most often decide whether an OSINT activity is lawful.
| Law or principle | What it says (in brief) | Why it matters for OSINT |
|---|---|---|
| Information Technology Act, 2000, Section 43 | A person who accesses a computer, system or network without permission of its owner or the person in charge is liable to pay compensation | OSINT stays on the right side by using what is publicly accessible. Bypassing log-ins or security is a different matter |
| IT Act, Section 66 | Doing any act in Section 43 dishonestly or fraudulently is an offence, punishable with imprisonment up to three years, a fine up to ₹5 lakh, or both | Turns unauthorised access done with dishonest intent into a criminal matter |
| IT Act, Sections 66C and 66D | Using another person’s password, electronic signature or unique identification feature fraudulently or dishonestly (66C); cheating by personation using a computer resource (66D). Each carries up to three years and a fine up to ₹1 lakh | Relevant to impersonation and misuse of someone else’s credentials or identity |
| IT Act, Section 69 | The Central or State Government, or an authorised officer, can direct interception, monitoring or decryption of information in a computer resource, on stated grounds such as sovereignty, security of the State, public order or investigation of an offence, with reasons recorded in writing | Shows that interception and monitoring have a formal route. It is separate from OSINT |
| IT Act, Section 69B | The Central Government may authorise monitoring and collection of traffic data for cyber security | Another formal route, again separate from OSINT |
| Digital Personal Data Protection Act, 2023 | Regulates processing of digital personal data. “Processing” covers collection, recording, organisation, structuring and storage, among other operations | OSINT that collects and organises information about identifiable people can fall within “processing” |
| Article 21 and the Puttaswamy judgment | In K.S. Puttaswamy v. Union of India (24 August 2017, (2017) 10 SCC 1), the Supreme Court held that privacy is a fundamental right. Any invasion must satisfy legality, a legitimate aim and proportionality | Shapes how State agencies are expected to collect and use personal information |
| Bharatiya Sakshya Adhiniyam, 2023, Section 63 | Sets out the certificate for electronic records produced as evidence | Decides whether OSINT material can be relied on in court |
| Platform terms of service | Contracts between users and platforms, often restricting automated collection | Not criminal law, but can lead to account bans or civil claims |
“Public” does not mean “free for any use”
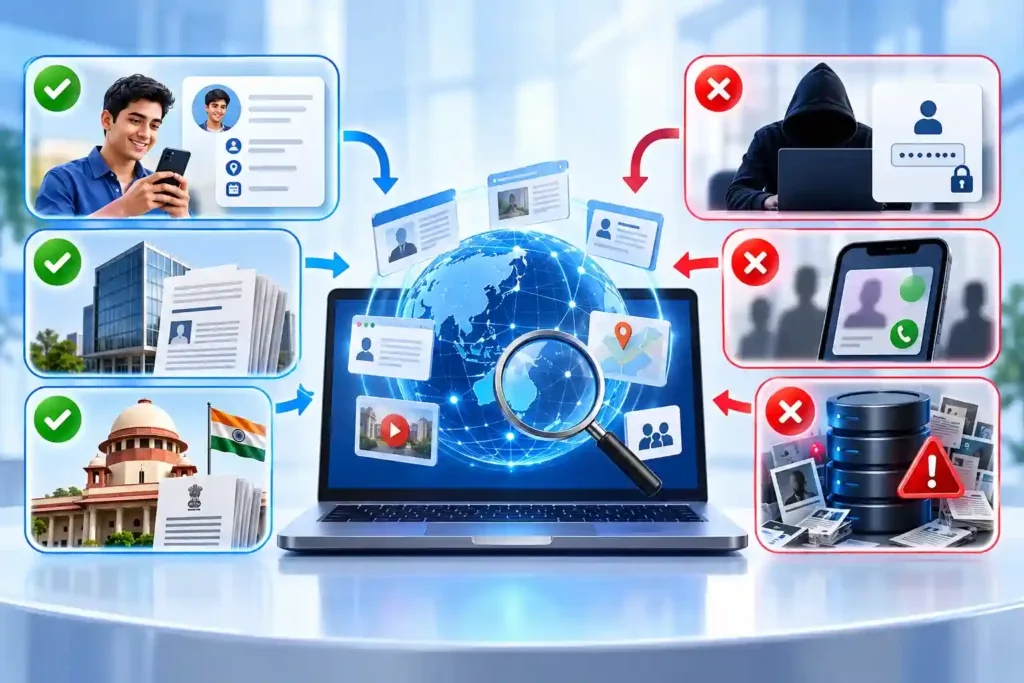
This is the point most people miss, so it deserves a closer look.
The DPDP Act excludes some publicly available personal data from its scope. Under Section 3(c)(ii), the Act does not apply to personal data that is made or caused to be made publicly available either (A) by the individual the data is about or (B) by any other person who is under a legal obligation in India to make it public.
That exclusion is narrower than “anything visible on the internet”. Compare:
| Situation | Likely position under Section 3(c)(ii) |
|---|---|
| A person posts their own details on a public profile | Within the exclusion, since the individual made it public |
| A company discloses director details in a statutory filing | Within the exclusion, as a legal obligation to make it public (confirm with counsel for the specific filing) |
| A third party posts someone else’s phone number or photo | Not clearly within the exclusion, since neither condition is met |
| Data from a leaked or breached database found online | Not within the exclusion, and carries wider legal risk |
So an organisation that collects data on individuals from many sources cannot assume that “it was online” settles the question.
When do the DPDP Act obligations start?
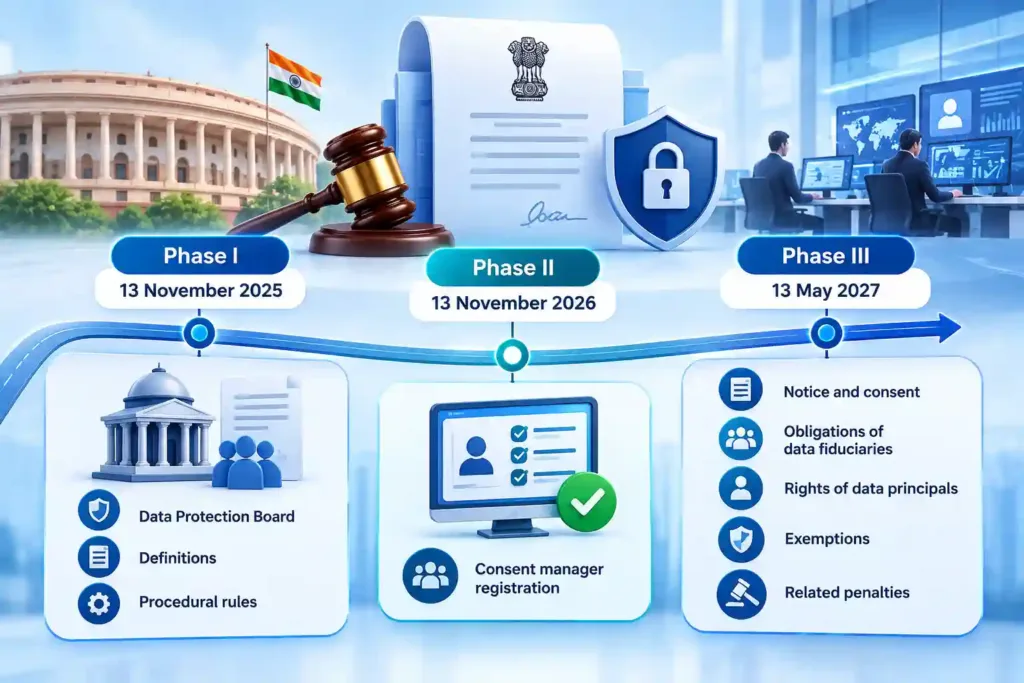
The DPDP Rules, 2025 were notified on 13 November 2025 and bring the Act into force in phases.
| Phase | Date | What starts |
|---|---|---|
| Phase I | 13 November 2025 | Institutional provisions such as the Data Protection Board, definitions and procedural rules |
| Phase II | 13 November 2026 | Consent manager registration |
| Phase III | 13 May 2027 | The main framework: notice and consent, obligations of data fiduciaries, rights of data principals, exemptions, and related penalties |
For private organisations running OSINT programmes, such as banks, enterprises and security vendors, the main obligations arrive in May 2027. Building the processes now is simpler than retrofitting them later.
For law enforcement and State agencies
Several points shape how State agencies think about OSINT.
Investigation powers apply
Viewing public information is generally treated differently from search, seizure or interception, which have specific conditions. Procedures and departmental directions remain the primary guide for any agency.
The privacy test applies
After Puttaswamy, any State action affecting privacy is expected to meet legality, a legitimate aim and proportionality. In practice this points to a clear purpose, a legal basis, and collection that is no wider than needed.
The DPDP Act has specific exemptions
Section 17(1)(c) provides that certain provisions do not apply where personal data is processed in the interest of prevention, detection, investigation or prosecution of any offence. Section 17(2)(a) allows the Central Government to notify instrumentalities of the State that are exempt in the interests of the sovereignty and integrity of India, security of the State and similar grounds. Which agencies and which provisions are covered is a legal question for each agency.
Interception is separate
Directions under Section 69 of the IT Act are for interception, monitoring and decryption, and need recorded reasons. They do not apply to reading public posts.
For banks, fintechs and enterprises

Private organisations use OSINT for due diligence, third-party risk, fraud checks, brand protection and threat monitoring. A few questions help keep this on firm ground.
- Purpose: Is there a specific, lawful purpose, such as fraud prevention or regulatory due diligence?
- Source: Is the information genuinely public, and was it made public by the person or by a legal obligation?
- Minimisation: Is only what is needed being collected, and for how long will it be kept?
- Accuracy: Are findings verified before they affect a decision about a person?
- Security: Is the collected data stored and access-controlled properly?
- Vendors: Do contracts with OSINT service providers define roles, security and data handling?
The grey areas
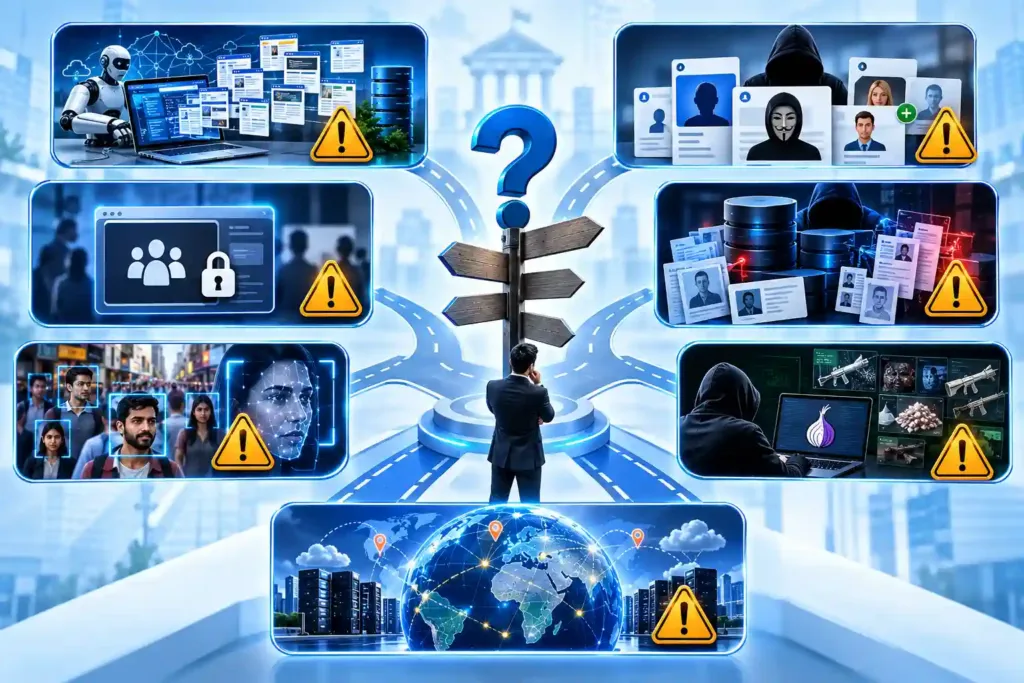
Some practices are not clearly prohibited but deserve extra care and often legal advice.
| Practice | Why it needs care |
|---|---|
| Large-scale scraping | May breach platform terms, and bulk personal data collection raises data protection questions |
| Fake or “sock puppet” profiles | Platform rules typically forbid them, and impersonation raises legal questions. Agencies usually follow their own authorisation and guidance |
| Joining closed or invite-only groups | The line between public and access-controlled can be thin |
| Using leaked or breached data | Provenance, lawfulness and admissibility can all be questioned |
| Facial recognition on public photographs | Biometric analysis of identifiable people raises privacy and proportionality questions |
| Dark web monitoring | Viewing is one thing, but interacting, purchasing or downloading illegal content is another |
| Cross-border data | Sources and storage may sit under other laws |
To my knowledge, Indian law does not give a clear, settled answer on several of these, which is why departmental guidance and legal review matter.
Myths and facts
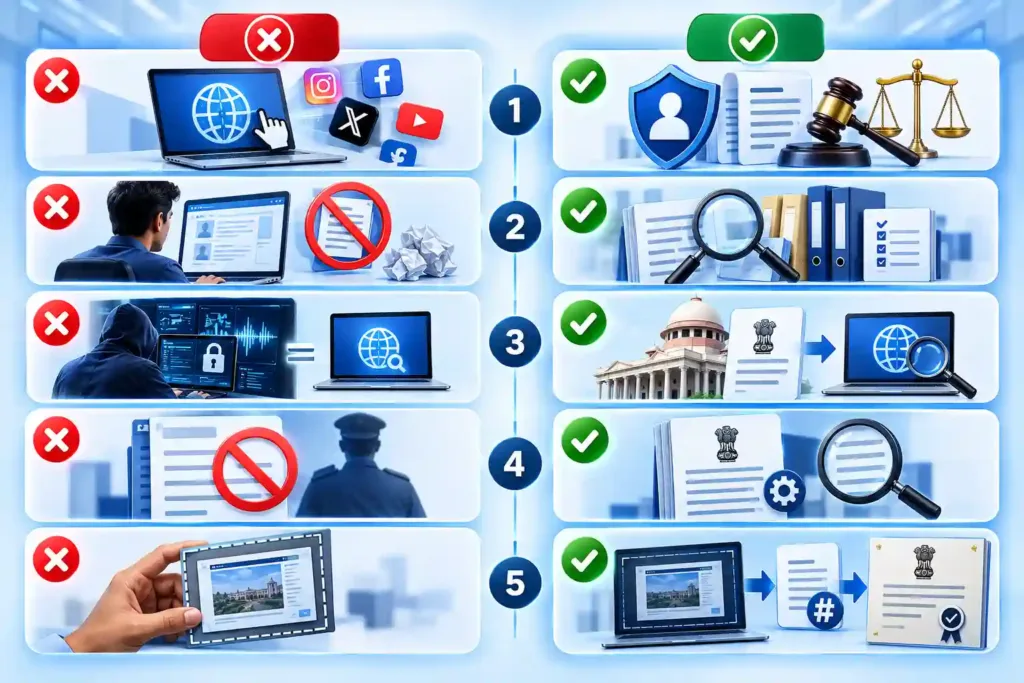
| Myth | Fact |
|---|---|
| “If it is online, anyone can use it however they like” | Public availability does not remove privacy, data protection, defamation or platform-terms issues |
| “OSINT needs no records because it is just browsing” | Without documentation, findings are hard to defend or reproduce |
| “OSINT and interception are the same” | Interception and monitoring need formal authority. OSINT uses public sources |
| “The DPDP Act exempts all investigation” | It has specific exemptions with conditions and notifications, not a blanket one |
| “A screenshot is enough evidence” | Electronic records need proper capture, hash values and a Section 63 certificate |
Making OSINT findings usable as evidence
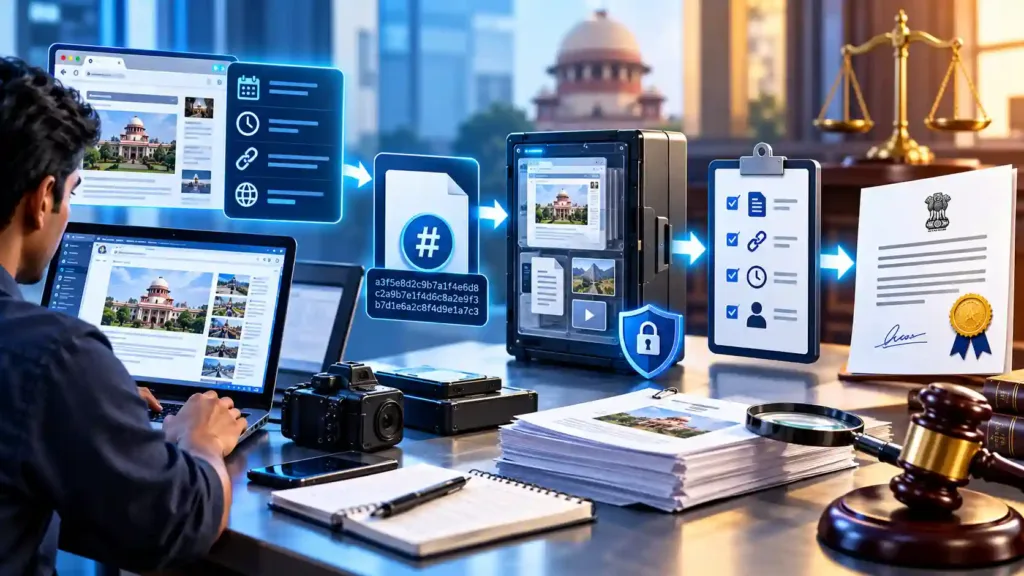
Lawful collection is only half the question. The other half is whether the material can be relied on later.
- Capture content with date, time, full URL and source where possible
- Record hash values and keep a capture log
- Preserve the original, not only a screenshot
- Prepare the Section 63 certificate for electronic records produced in proceedings
Our guides on the Section 63 BSA certificate and chain of custody for digital evidence under BNSS cover these steps.
A practical checklist
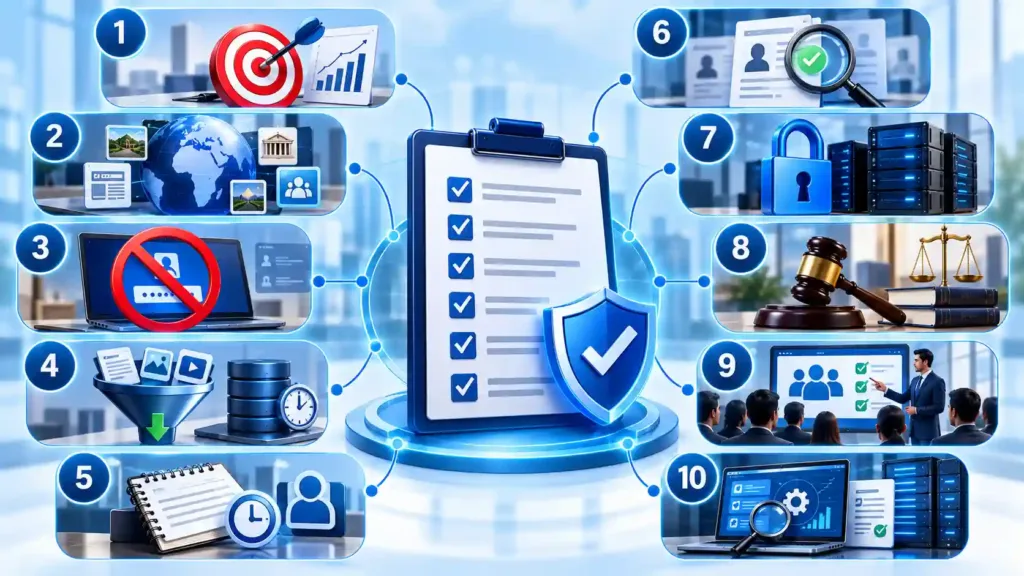
Many organisations that run OSINT programmes adopt practices like these.
| Area | Common practice |
|---|---|
| Purpose | Record the purpose and legal basis for each investigation or monitoring project |
| Sources | Limit collection to genuinely public or authorised sources |
| Access | Avoid bypassing log-ins, paywalls or security controls |
| Minimisation | Collect what is needed, and set retention limits |
| Records | Keep logs of what was collected, by whom, when and how |
| Verification | Confirm findings before acting on them or sharing them |
| Security | Control access to collected data and protect it |
| Review | Have legal counsel review the programme, especially grey areas |
| Training | Make sure analysts know the boundaries |
| Tools | Prefer tools that support logging, access control and auditability |
Disclaimer: General information, not legal advice. The position described here is as of October 2026. Specific cases and policies should be reviewed with legal counsel.
Frequently asked questions
1. Is OSINT legal in India?
Generally yes. Collecting and analysing genuinely public information is not unlawful, and no Indian law bans OSINT by name. Legality depends on how the information is collected, whether it includes personal data, who is collecting it, and how it is used.
2. Is it legal to scrape websites and social media in India?
There is no dedicated Indian statute on scraping. Platform terms often restrict it, and collecting personal data at scale raises data protection questions. Accessing anything protected by log-ins or security controls can also raise IT Act issues. Legal advice is recommended for any large-scale collection.
3. Can police use public social media posts in an investigation?
Public posts can be viewed and analysed as part of an investigation, within the agency’s own procedures and the privacy test of legality, legitimate aim and proportionality. Where posts are to be used as evidence, they need to be captured and certified properly.
4. Does the DPDP Act apply to OSINT?
It can. The Act regulates processing of digital personal data, and collecting and organising information about identifiable people falls within “processing”. Personal data that the individual has made public, or that is made public under a legal obligation, is excluded under Section 3(c)(ii). The main obligations begin on 13 May 2027, and State agencies have specific exemptions.
5. Is using a fake profile for OSINT legal?
It is a grey area. Platform rules usually prohibit fake profiles, and impersonation can raise legal questions. State agencies typically work under their own authorisation and guidance, and private organisations are advised to take legal advice first.
6. Is dark web monitoring legal?
Monitoring publicly accessible dark web content is generally treated like other open source research. Buying illegal goods, downloading unlawful material or interacting with criminals is a different matter and carries legal risk.
7. Is OSINT the same as surveillance or interception?
No. OSINT uses information that is publicly available. Interception, monitoring and decryption of communications need formal legal authority, such as directions under Section 69 of the IT Act.
8. Is OSINT admissible as evidence in India?
It can be, if collected lawfully and documented properly, with hash values, a capture record and a Section 63 certificate under the Bharatiya Sakshya Adhiniyam, 2023, where electronic records are produced.